Product — Control
Let the agent work inside explicit operational boundaries.
Roles and permissions, named specialists, agent policy, rules for reaching private systems, preview and approve, secrets and credentials, audit and cost.
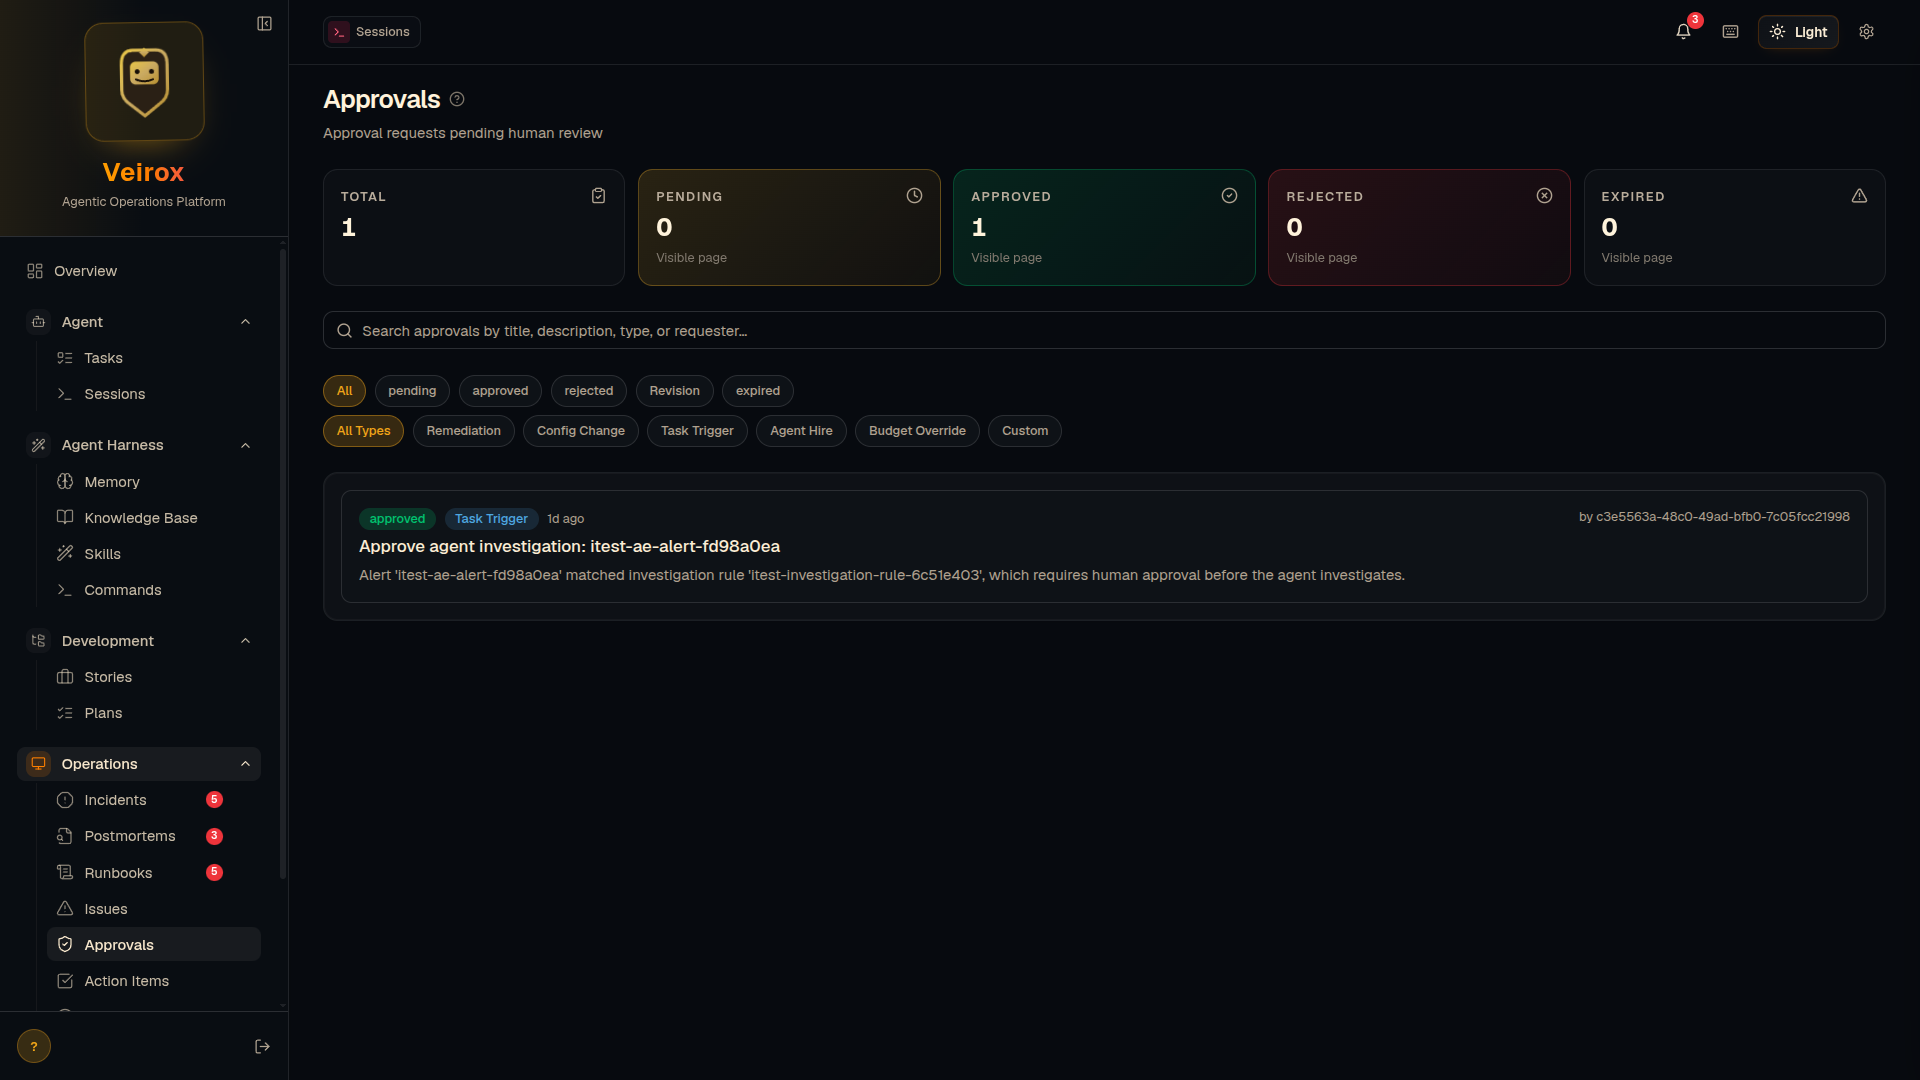
Roles and permissions
Owner, admin, member, and viewer roles govern the single instance — the whole access-control model.
Named specialists, published deliberately
Give different kinds of work their own named configuration — its own instructions and boundaries — and publish changes on purpose. Work already in progress keeps the version it started with. Point a specific area of work, like who leads a war room, at a chosen specialist by default.
Specialists can call in help
A specialist that needs a different kind of expertise can hand a piece of the work to another one directly, still operating inside the same boundaries the whole time.
Agent policy
Control what the agent is allowed to do on its own, and what needs a person's approval first.
Rules for reaching private systems
Allow, deny, or require-approval rules for anything touching private infrastructure, tested before you rely on them.
Preview and approve
See the proposed action and decide in the console or through a time-limited public action link.
Secrets and credentials
Stored as references and resolved only at the moment they're needed — never embedded in a task or config.
Audit, governance, and cost
A scrubbed audit history, retention controls, security settings, and daily model-spend ceilings.